

A jury at the federal court in Manhattan found a 36-year-old security consultant from Maryland guilty of computer fraud and money laundering on October 7, 2026. In 2021 he had drained around $53.3 million from the decentralised exchange Uranium Finance in two attacks, according to the prosecution. His defence argued that he had called only publicly accessible functions of the smart contract, forged no credentials and deployed no malicious code. The jury took a little over two hours to decline that line.
For holders in Germany this is not a ruling about their portfolio but one about the basis on which DeFi operates. Putting coins into a liquidity pool means leaving the space where a supervisor sets rules and entering one where the programme code alone determines payout. Whether exploiting a flaw in that code amounts to a crime or merely to clever play within the rules had been an open question until this Wednesday. It has now been answered by an American court under American law, and that is exactly how far the answer reaches.
A liquidity pool is a smart contract into which users deposit two tokens so that others can swap between them; the depositors receive a share of the trading fees in return. Uranium Finance ran such pools on BNB Chain, the network behind BNB, and had derived its code from well-known templates.
The Arithmetic Flaw in the Pair Contract: 26 Liquidity Pools in One Series of Attacks
The pair contract is the contract that holds the reserves for exactly one token pair and recalculates on every swap how much may leave. At Uranium Finance that recalculation was out by a factor of one hundred, according to analyses from 2021: the contract believed its own holdings to be a hundred times larger than they were. Anyone who knew this could put in a very small amount and take out a very large one.
The flaw was introduced during a migration to a new contract version. The project had asked its users shortly beforehand to move their deposits into that new version, and the attack landed in the middle of the move. The first strike came on April 8, 2021 and took around $1.4 million, achieved through a series of calls to the reward function. The second attack on April 28, 2021 then hit 26 pools at once and forced the protocol to shut down.
The sums diverge across the coverage, and that should not be smoothed over. The prosecution cites around $53.3 million for the second attack. Trade publications add both attacks together and arrive at $54.7 million to just under $55 million. An incident database from 2021 puts the damage at $57.2 million. The range of $53.3 million to $57.2 million is therefore the honest figure.
What happened before the attack is striking: the team says it suspected a critical flaw might exist without having found it. Several reviews of the code had not identified it as critical.
“Code Is Law” as a Defence: The Jury Needed Just Over Two Hours
“Code is Law” is the notion that in an open protocol only what the programme code permits applies, and that there is no further rule left to break. On that reading the attacker had merely done what the contract offered, and the loss would be a design error on the depositors’ part.
In court this became the argument that there had been no deception and no break-in, because every function used was public and callable by anyone. The jurors did not follow it. A deliberation of a little over two hours across two counts shows how little they saw to argue about. Reports on the trial describe the outcome explicitly as a rejection of that line of defence (Cryptopolitan).
What the verdict contains reaches beyond this case. It separates two things that often merge in the DeFi debate: whether a transaction is technically possible, and whether it is permitted. Until now the two could be equated, with the argument that a protocol without an operator also lacks house rules. A jury has now dismissed that argument.
Computer Fraud and Money Laundering: The Two Guilty Verdicts in Detail
The defendant was found guilty on both counts of the indictment. The first is computer fraud and relates to the two attacks themselves. The second is money laundering and relates to what happened to the money afterwards.
The statutory maximum penalties stand at ten years for the computer fraud and twenty years for the money laundering, according to the prosecution. The office itself stressed that these ceilings are set by the legislature and that the actual sentence is for the court alone. The verdict covers guilt, not punishment.
Why the Money Laundering Count Is the Heavier One
That concealment carries a higher maximum penalty than the act itself looks skewed at first, but the reason holds up: computer fraud describes a single access, money laundering a chain of acts over years. Sending stolen tokens through a mixer and then converting them into physical assets means building that chain piece by piece yourself.
Tornado Cash, Trading Cards and Roman Silver Coins: The Route the Proceeds Took
A mixer is a service that blends deposits from many users and pays them out later, so that the link between the origin and the destination of a transfer can no longer be traced on the blockchain. Tornado Cash is the best-known of these services on Ethereum. According to the indictment, parts of the proceeds passed through it.
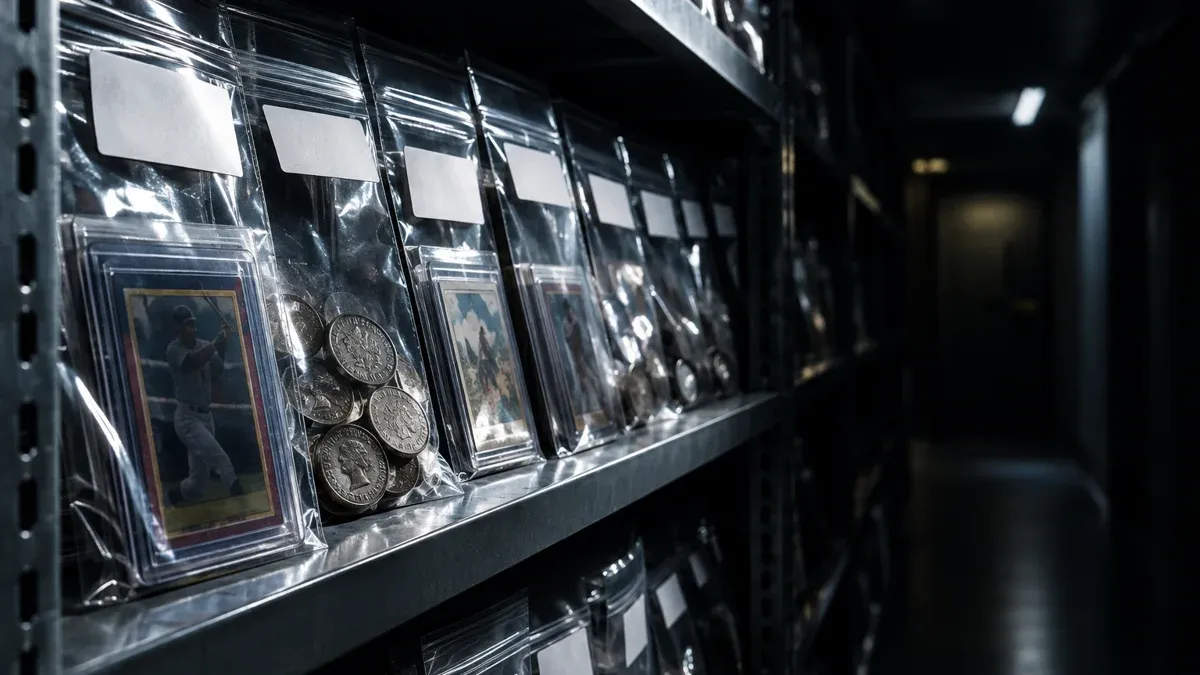
After that, crypto turned into something you can hold. The prosecution cites a Black Lotus trading card bought for $500,000 and antique Roman coins for $601,545. This step is the most welcome one for investigators: a card has a seller, an invoice, a shipping route and often an auction catalogue. The mixer blurs the trail on the chain; the purchase lays it bare again off the chain.
A lesson hangs on precisely that, and it reaches beyond the single case. A mixer’s anonymity ends at the point where the money leaves the crypto world. The larger the sum, the harder it is to spend inconspicuously, and the more certainly a record with a name on it comes into being.
$31 Million Seized: What Victims of a DeFi Exploit Realistically Recover
On February 24, 2025 the authorities seized crypto assets worth around $31 million, valued as at that date. Measured against the range of $53.3 million to $57.2 million, roughly half is therefore back within the state’s reach. Whether seized money ends up with the depositors is another matter: it goes first into a proceeding, and any distribution to victims requires separate applications, evidence of your own deposit, and time.
Uranium Finance ceased operations after the second attack. An abandoned protocol has no legal department, no customer service and no balance sheet from which compensation could be paid. Anyone who had deposited there stood without a counterpart for five years and today holds a guilty verdict but no payment.
The scale of the problem is growing. Our analysis of the quarterly figures shows that crypto hacks cost $1.26 billion in three months alone, the highest level of 2026. A verdict five years after the act changes little in that calculation.
MiCA Does Not Cover Decentralised Protocols: The Difference from a Licensed Exchange
MiCA is the EU regulation that subjects providers of crypto services to licensing and supervision. It addresses companies with a counterparty, not code. Legal commentary describes the exemption for genuine DeFi protocols narrowly: it applies where an offering is decentralised technically and in its governance, runs solely through smart contracts, and has no legal entity acting as counterparty. Where founders retain intervention rights or collect fees, an operator position requiring a licence can still arise in the individual case.
In practical terms: on a licensed exchange you have a contractual partner with a registered seat, a supervisor, a complaints route and duties to segregate client funds. In a pool you have a contract. Anyone wanting to hold both side by side will find the licensed houses in our comparison of regulated crypto exchanges; the pool side stays untouched by that, because it belongs to nobody.
What Supervisors in Germany Do and What They Do Not
Germany’s BaFin publicly warns against unlicensed offerings that present themselves as DeFi staking. A flaw in the code of a genuinely decentralised protocol, by contrast, falls into no remit that any authority could repair. Nobody there can suspend trading, freeze an account or reverse a payout.
Audit Passed, Flaw Remained: What a Smart Contract Audit Covers
A smart contract audit is a paid review of contract code by third parties, meant to find errors and attack routes before money flows in. At Uranium Finance, according to the later post-mortem, several reviews had not flagged the decisive flaw as critical.
That does not make audits worthless, though it puts them in proportion. An audit relates to a particular version of the code on a particular date. Every migration after that is unreviewed until it is reviewed again, and at Uranium Finance the flaw entered the system through exactly such a migration. Audited code is therefore a snapshot and not an assurance about the version your money sits in tomorrow.
How to recognise a solid audit comes down to two questions: is the review report public in full and dated, and does it relate to the contract address your money sits in today? If either is missing, the audit covers something other than your stake.
German Law and the Exploit: The Case Sets No Precedent Here
The conviction was handed down under American law, and an American jury verdict binds no German court. On the state of the published legal commentary, there is as yet no ruling by Germany’s highest courts on whether exploiting a smart contract flaw is a criminal offence.
Legal commentary from law firms frames the question differently in Germany than the American indictment does. On that account a pure programming error is no offence in itself; it becomes punishable only where deception is added or where there is interference with another party’s data, for which the data alteration offence under Section 303a of the Criminal Code is cited. In every variant, intent has to be proven, and that is considered difficult with contracts that execute automatically. This framing comes from advisers rather than a court, and should be read accordingly.
Anyone in Germany who falls victim to an exploit therefore faces an uncomfortable finding: criminal liability is unsettled, the perpetrator is often unknown, and the protocol may no longer exist. Filing a police report remains worthwhile, because it puts the act on record and can form the basis for a late distribution of seized funds. Quick money rarely follows.
The Loss Remains a Separate Problem for Tax Purposes
A loss from an exploit is not a sale, and whether it can be claimed for tax depends on the individual case and on the documentation. Records of the deposit, its timing and its size count for more here than the legal question. Anyone not already keeping a complete log of their movements will find the programmes that produce exactly this evidence in the crypto tax software and portfolio tracker comparison.
Custody and Counterparty Risk: Where Your Coins Actually Sit in a DeFi Pool
Counterparty risk is the danger that whoever holds your assets cannot return them. In a pool you hold no coins but a claim against a contract, and that claim is exactly as sound as the arithmetic inside it. At Uranium Finance the arithmetic was out by a factor of one hundred, and the claim was worthless before anyone could react.
That mechanism yields a plain division of holdings, one that has nothing to do with a market view. Whatever is meant to sit for the long run belongs in your own custody, where no third-party contract and no third-party balance sheet stands in between. Which devices manage that and what they cost is set out in our hardware wallet comparison. Whatever works in a pool is a stake carrying total-loss risk, however high the advertised yield looks.
A second consequence concerns approvals. Granting a contract unlimited access to a token once leaves that door open even after you have long since withdrawn your deposit. Revoking such approvals regularly costs minutes and limits the damage if a contract later fails.
The February 16, 2027 Date: A Sentence of Up to Twenty Years Still Open
Sentencing is set for February 16, 2027. Until then guilt is established and the length of the sentence is not, and the ten and twenty years cited are statutory ceilings rather than a forecast. Reports on the trial place the case in a run of American proceedings in which courts increasingly treat crypto theft like conventional property crime (Crypto Briefing).
For the European market the next date is a different one. As long as the EU rules leave decentralised protocols out, responsibility for vetting a pool shifts entirely to the depositor. A verdict in Manhattan changes nothing about that, and therein lies the actual news of this Wednesday.
DeFi Exploit Verdict: $53.3 Million and No Pause Button
The guilty verdict answers a question that stood open for five years, and it answers it against the attackers. For the depositors’ position it changes little: a pool without an operator has nobody who is liable when something goes wrong, and the money was gone before the court even acquired jurisdiction.
- Separate holdings from stakes. What you intend to hold belongs in your own custody rather than in a contract you have not read. The devices for it and their prices are in the hardware wallet comparison.
- Establish who your counterpart is. Where a licensed counterparty exists, there is supervision and a complaints route; in a pool there is neither. The licensed houses are listed in the comparison of regulated crypto exchanges.
- Document every deposit immediately. Without evidence of the timing and size of your deposit, neither a distribution of seized funds nor a tax treatment of the loss is enforceable. The crypto tax software comparison lists the suitable programmes.
(As of October 8, 2026. This article is not investment advice. Prices and fee structures change; check the terms with the provider before you buy.)



Be the first to comment