


Former Mt. Gox CEO Mark Karpelès criticized Ledger’s response to hardware implant warnings, questioning whether earlier communication could have prevented losses.
Karpelès said Ledger received reports of spy hardware implants as early as December 2025. He accused the firm of responding inadequately.
According to him, Ledger’s only response was a blog post about a compromise in March 2026.
For him, Ledger could have done more to prevent the CryptoBillis incident, where users lost over $90M.
I do know a better communication on this at the time could have saved 90+ million USD in losses. I know it’s a difficult job, but I can’t fathom how you could have failed to be alarmed by mass-produced advanced implants.
On his part, Ledger’s Gauthier read this as virtue signalling, not genuine criticism, and called out Karpelès’ past failure at the Mt. Gox exchange.
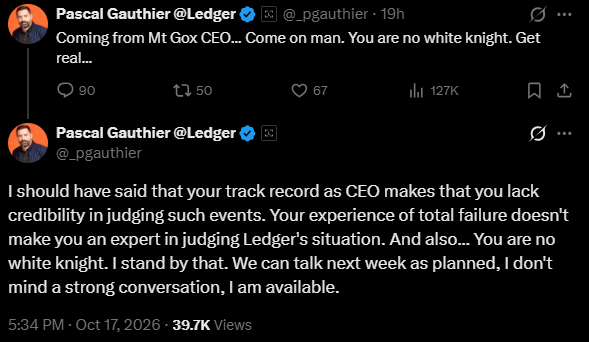
The interaction between the two got too personal and veered off the crucial topic: Was the Ledger supply chain compromise and +$90M in stolen funds avoidable?
Community blasts Ledger for slow response
Mark Karpelès strongly believes that the unfortunate supply chain attack could have been stopped based on the early ‘five-alarm fire’ warnings. While accepting his shortcomings at Mt. Gox, Karpelès added,
I was hoping you guys were better than that. I’ve been holding Ledger to a higher standard than what happened at Mt. Gox, because I trusted you to do better by learning of my failure – to be better than me.
He also accused Ledger of “downplaying the incident” as isolated to reseller CryptoBillis, despite reports of similar implants in other regions.
Ledger disputed reports of European exposure after analyzing a reported case in Germany.
However, Karpelès maintained that the attack extended further. He said he had helped several users check their devices for compromise.
He urged Ledger to provide clearer disclosures:
There might be a good reason for that (denying implants in other regions), but an end user doesn’t know that, and shouldn’t have to worry if their device is altered or not
Surprisingly, the community sided with Karpelès and pressed Ledger for more transparency.
What does the Ledger attack mean for buyers?
In early October, Ledger confirmed devices sold by reseller CryptoBillis had unauthorized implants that scan and send seed phrases to a private server. It paused sales from CryptoBillis and the broader Southeast Asian region as losses crossed $100M.
As a precaution, several players in the sector, including Trezor and OneKey, removed third-party resellers and tightened distribution checks.
Crypto was spawned out of distrust of government and centralized entities, with self-custody as its foundation to give users full control over their assets. But with ongoing self-custody security risks, more will be forced to go back to safer centralized custodians.
Final Summary
- Mt. Gox CEO blasted Ledger for ‘downplaying’ its supply chain attack
- Ledger maintains the compromise is isolated to the Southeast Asian region, but others claim the attack is global


Be the first to comment