

Crypto security losses have climbed into the billions in 2026, exposing a threat landscape that extends far beyond traditional DeFi exploits. Hundreds of incidents have targeted protocols, wallets, exchanges and critical infrastructure, while a small number of mega-breaches have driven a disproportionate share of stolen funds. Infrastructure attacks, private-key compromises, social engineering and AI-powered scams are adding new layers of risk.
This Coinpedia’s report examines where crypto is losing the most money in 2026, which attack vectors are causing the largest damage, and how the security threat is evolving across the industry.
2026 Has Already Become a Multi-Billion-Dollar Security Story
The 2026 security record already includes 288 reported incidents and roughly $2.21 billion in losses, spanning publicly reported exploits, protocol failures and incidents involving intermediaries. The attack surface now extends across exchanges, wallets, infrastructure, operational systems and smart contracts.
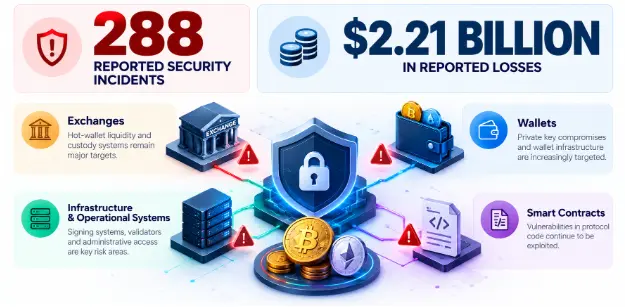
Crypto platforms increasingly depend on infrastructure that sits behind the blockchain. Exchanges hold hot-wallet liquidity, protocols rely on transaction-signing systems, and development teams control deployment and administrative access. A compromise at any of these points can expose large pools of assets without requiring a conventional smart-contract exploit.
The largest losses in 2026 have involved systems capable of authorizing transactions, controlling wallets, validating activity or influencing protocol behavior.
Attack Frequency Is Rising Faster Than the Dollar Damage
H1 2026 recorded 207 hacks, compared with 83 during H1 2025. Yet total losses fell to about $972 million from approximately $2.3 billion a year earlier, showing that the number of attacks rose even as aggregate damage declined.
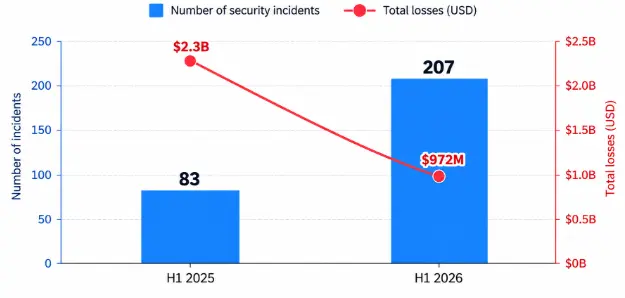
Smart-contract exploits accounted for 125 of the 207 H1 incidents, making them the most common attack category. The expanding number of protocols, applications and financial products has also widened the number of potential entry points available to attackers.
The median H1 2026 hack was around $219,000, while the mean loss reached roughly $4.7 million. The wide gap reflects the impact of several extremely large breaches on the overall average. Smaller exploits account for a high volume of incidents, while a limited number of major compromises drive a much larger share of the money stolen.
A Small Number of Attacks Is Driving Most of the Damage
Approximately 4% of attacks accounted for about 75% of stolen funds during H1 2026. Most financial losses were therefore concentrated in a small group of major incidents.
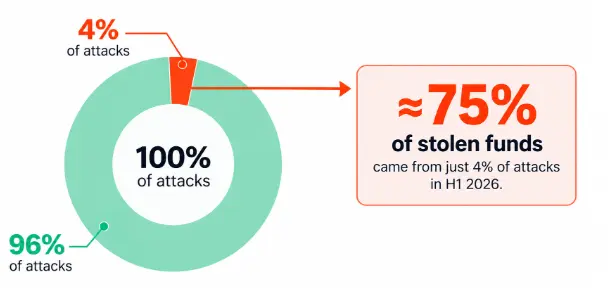
The concentration was particularly visible in April, when breaches involving Drift and KelpDAO together accounted for roughly $577 million in losses. Many other attacks during the period involved significantly smaller amounts.
The data points to two distinct security pressures. Protocols face a continuous stream of lower-value exploits, while high-value infrastructure and custody failures can produce hundreds of millions of dollars in losses through a single compromise.
Infrastructure, Not Just Smart Contracts, Is Driving the Biggest Losses
Smart-contract exploits accounted for most H1 incidents, but infrastructure and operational compromises were responsible for roughly 76% of stolen funds while accounting for only about 15% of incidents.
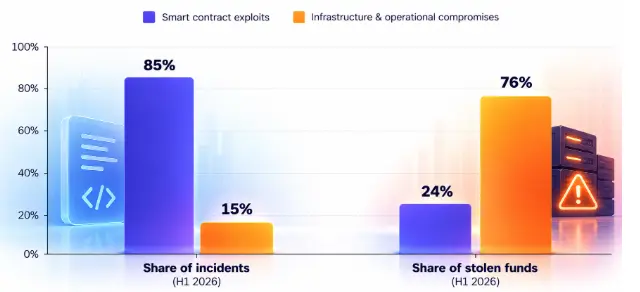
These attacks target private keys, signing systems, credentials, wallet infrastructure, privileged accounts and transaction-approval processes. A weakness in any of these layers can give attackers control over assets without exploiting the underlying smart contract.
A protocol can have audited contracts while remaining exposed through its developer environment, front end, key-management system or transaction-signing architecture. Security controls therefore need to cover both the code layer and the systems that authorize changes and transactions. Access permissions, key segregation, multi-party approvals and transaction monitoring become critical when large asset pools are involved.
The Biggest Breaches Are Hitting Critical Crypto Infrastructure
The largest security incidents of 2026 include major compromises of infrastructure and asset-control systems. Liquid Network suffered a roughly $319 million gross theft after attackers exploited validator software to create unbacked synthetic bitcoin and convert it into real BTC. Around 85% of the funds were subsequently returned.
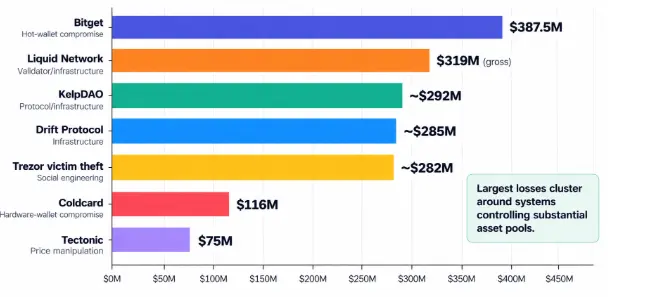
KelpDAO and Drift suffered losses in the $285 million–$292 million range, while Bitget reported approximately $387.5 million in affected assets following unauthorized hot-wallet transfers.
Coldcard also suffered a compromise involving approximately $116 million, adding hardware-wallet infrastructure to the year’s major security incidents. The incidents involved different attack methods, but each reached systems connected to substantial pools of assets. Custody controls, transaction authorization, key management and rapid containment can materially affect how much an attacker is able to move.
Security Audits Are Not a Complete Defense
Security audits address a major part of smart-contract risk, but audited platforms can still suffer significant losses. A sample of 245 documented incidents from January 2025 through July 2026 found that 147 involved platforms that had completed independent audits. Those platforms accounted for 88.44% of the capital drained in the sample.
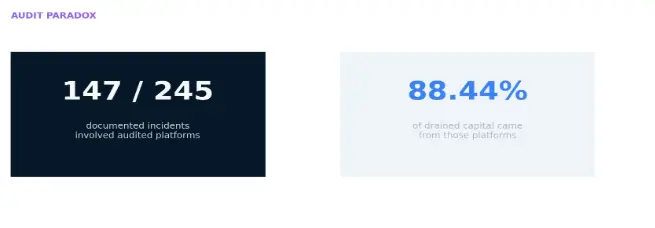
The losses included risks outside traditional contract review, including compromised infrastructure, private keys, malicious integrations, governance failures and social engineering. Security therefore requires controls beyond code review, including infrastructure hardening, access management, transaction monitoring, privileged-account protection and incident response.
Insurance Capacity Is Tiny Compared With the Loss Surface
Active coverage across major on-chain insurance protocols fell 20.2%, from $163.2 million to $130.2 million, while cumulative payouts remained around $33 million.
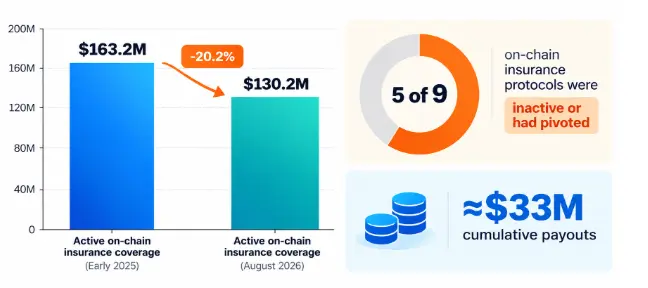
The available coverage remains small compared with the industry’s multi-billion-dollar security losses. Centralized platforms may maintain individual protection funds, but those reserves generally apply to specific ecosystems rather than providing broad market-wide protection.
Insurance also becomes relevant only after a security event has occurred. Coverage limits, exclusions, claim requirements and the assets covered determine how much of a loss can actually be recovered.
AI Is Expanding the Human-Compromise Layer
AI is making established forms of crypto crime faster and more convincing. AI adoption across crypto crime reached 54 out of 100 in 2026, up from 28 in 2024.
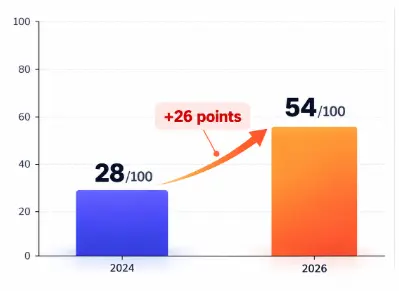
The technology is being used across phishing, synthetic identities, deepfake communications, reconnaissance and social engineering. These methods can target employees, developers, signers and users with legitimate access to sensitive systems.
A compromised employee credential can open a production environment. A manipulated signer can authorize a transaction. A convincing deepfake or fabricated communication can bypass normal trust checks.
What the 2026 Security Record Reveals
The biggest crypto security risks are shifting from code alone to the systems that control and move assets. Smart-contract exploits remain the most common attack type, but infrastructure, custody, private keys, transaction controls and market-pricing systems are producing some of the largest losses. A relatively small number of major breaches can also outweigh hundreds of smaller incidents in financial damage.
The 2026 record points to a broader security perimeter across the crypto industry, one that includes code, infrastructure, capital controls and human access. Protecting each layer is becoming increasingly important as more assets move through interconnected protocols, exchanges and automated financial systems.



Be the first to comment