

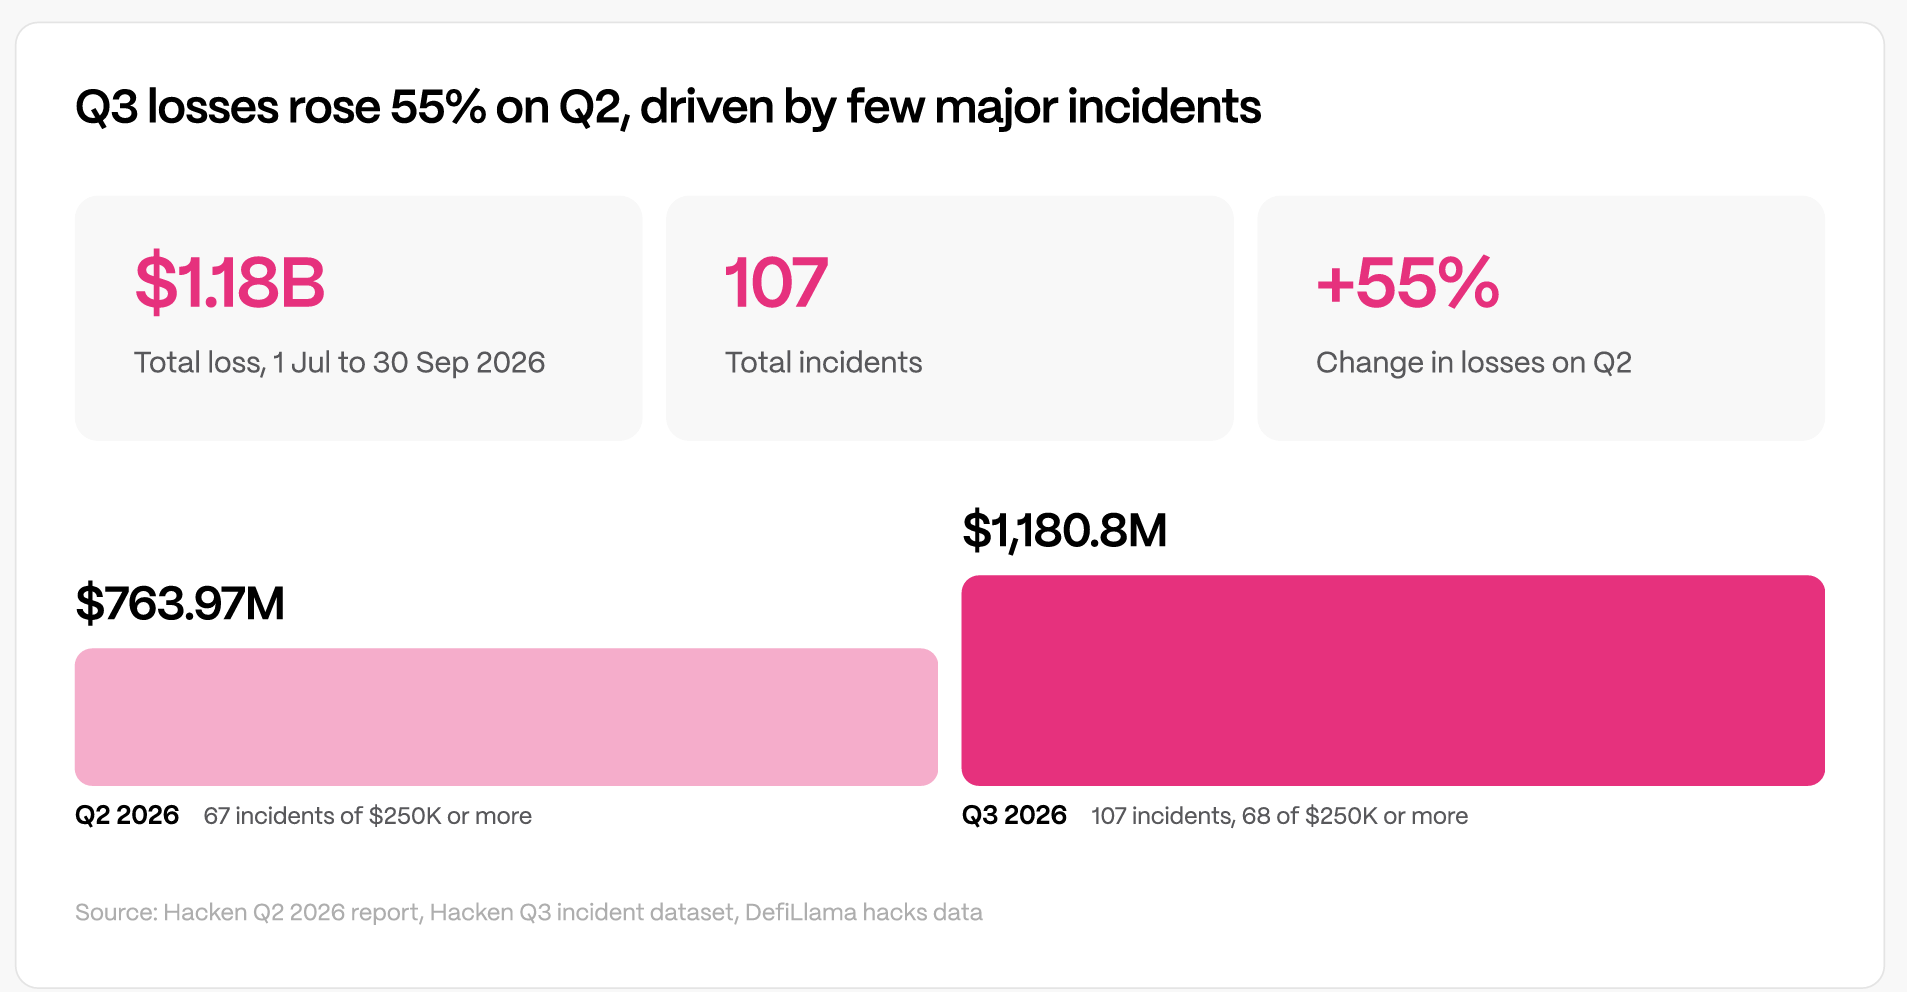
Crypto security risks intensified in Q3 2026, as both the number of incidents and the financial damage increased. Losses grew by an astonishing 55% to $1.18 billion from $ 763.97 million. This was a staggering 40% growth rate that occurred during one quarter.
Moreover, the number of reported breaches grew from 67 in Q2 to 107 in Q3. Of those 107 breaches, 63 were associated with losses exceeding $250,000.
Therefore, it appears that this represents an increase in potential vulnerability as well as increasing financial risk. However, there is evidence that the majority of the damage has been limited to fewer large-scale incidents.
Additionally, compromised suppliers, delayed patches, and un-audited components were responsible for 77% of losses, worth $906.8 million.
Therefore, it is evident that hackers are exploiting vulnerabilities beyond the simple exploitation of smart contract code. They are exploiting vulnerabilities within third-party systems and operational processes.
Stronger audits must therefore include suppliers, timely patching, and continuous monitoring across connected infrastructure.
The flaws behind Q3’s crypto losses
These broader security gaps become clearer when examining how attackers exploited specific weaknesses and how much each failure cost. Smart contract defects led to 79 reported breaches, which resulted in approximately $569.5 million in losses.
On the other hand, access control and operational failures resulted in a mere 22 breaches totaling $477.6 million. Therefore, they produced more financial impact per breach.
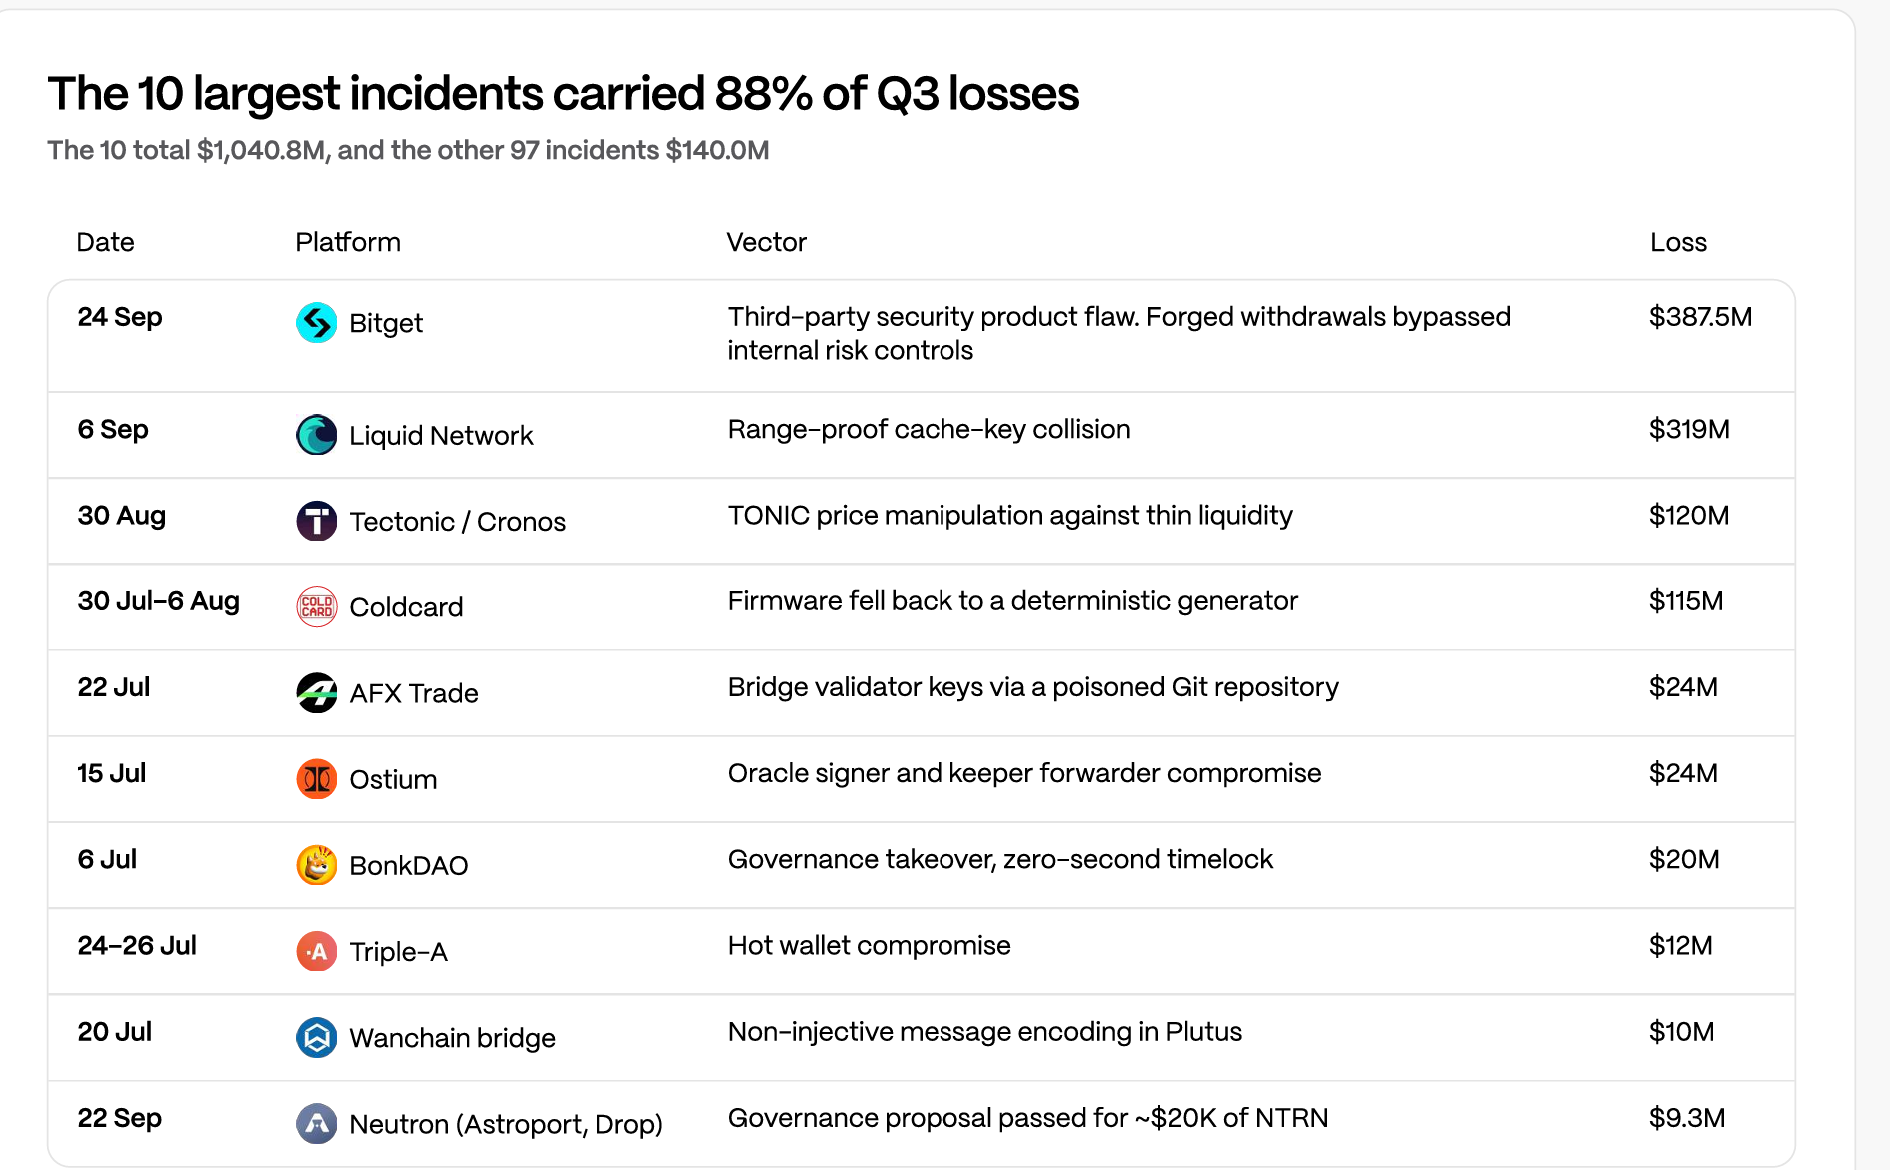
Bitget accounted for the biggest loss, losing approximately $387.5 million. This was after hackers exploited a zero-day flaw in a third-party security software package to generate fraudulent withdrawal requests.
Additionally, the Cosmos EVM chain lost approximately $5.7 million due to its failure to implement a security update within 96 days of its release. This created a window of opportunity for underflow exploits against chains that had not yet implemented the security update.
Similarly, Coldcard suffered $111 million in losses after a build check flaw introduced a weakness into hardware wallet seed generation. However, this type of error should have been identified and addressed through proper software configuration procedures before use.
Can monitoring stop crypto hacks?
With the causes of these attacks clear, looking forward, the next question is whether continuous monitoring can stop similar losses. According to Hacken research, attackers exploited weaknesses even after security fixes became public.
This suggests that companies often failed to act quickly enough, rather than failing to identify the risks. Continuous monitoring could help teams track new threats, fix urgent weaknesses, and confirm that updates reach all affected systems.
For crypto firms, these changes could reduce theft, recovery costs, and service disruptions. Ultimately, constant monitoring needs to result in a quicker response time for addressing potential issues before they become actual problems.
Final Summary
-
Crypto security losses rose 55% to $1.18B in Q3 2026, with infrastructure and patching gaps driving 77% of losses.
-
Crypto firms need continuous monitoring and faster patching to prevent repeat attacks and reduce financial damage.


Be the first to comment