

Lookalike payment addresses targeted nearly 4.5 million Solana wallets over 11 months, according to blockchain-data firm Bitquery’s Oct. 9, 2026 findings. The findings show why a successful small test transfer can still precede a much larger payment to a scammer.
The technique, known as address poisoning, plants a misleading entry in a wallet’s payment history. A tiny incoming transfer puts the sender’s lookalike address near a legitimate payment. If the user later copies that address, they can send money to the wrong recipient.
Ethereum metrics hit record high because of cheap gas fees – because of this massive scam
A Solana test transfer can reach the wrong address
Bitquery describes a Nov. 17, 2025 case in which a wallet first paid $10 in USDT to its Gate.io deposit address. A lookalike sent dust 12 seconds later. The wallet then sent a second $10 test to the fake, followed by 30,749.80 USDT to that same address.
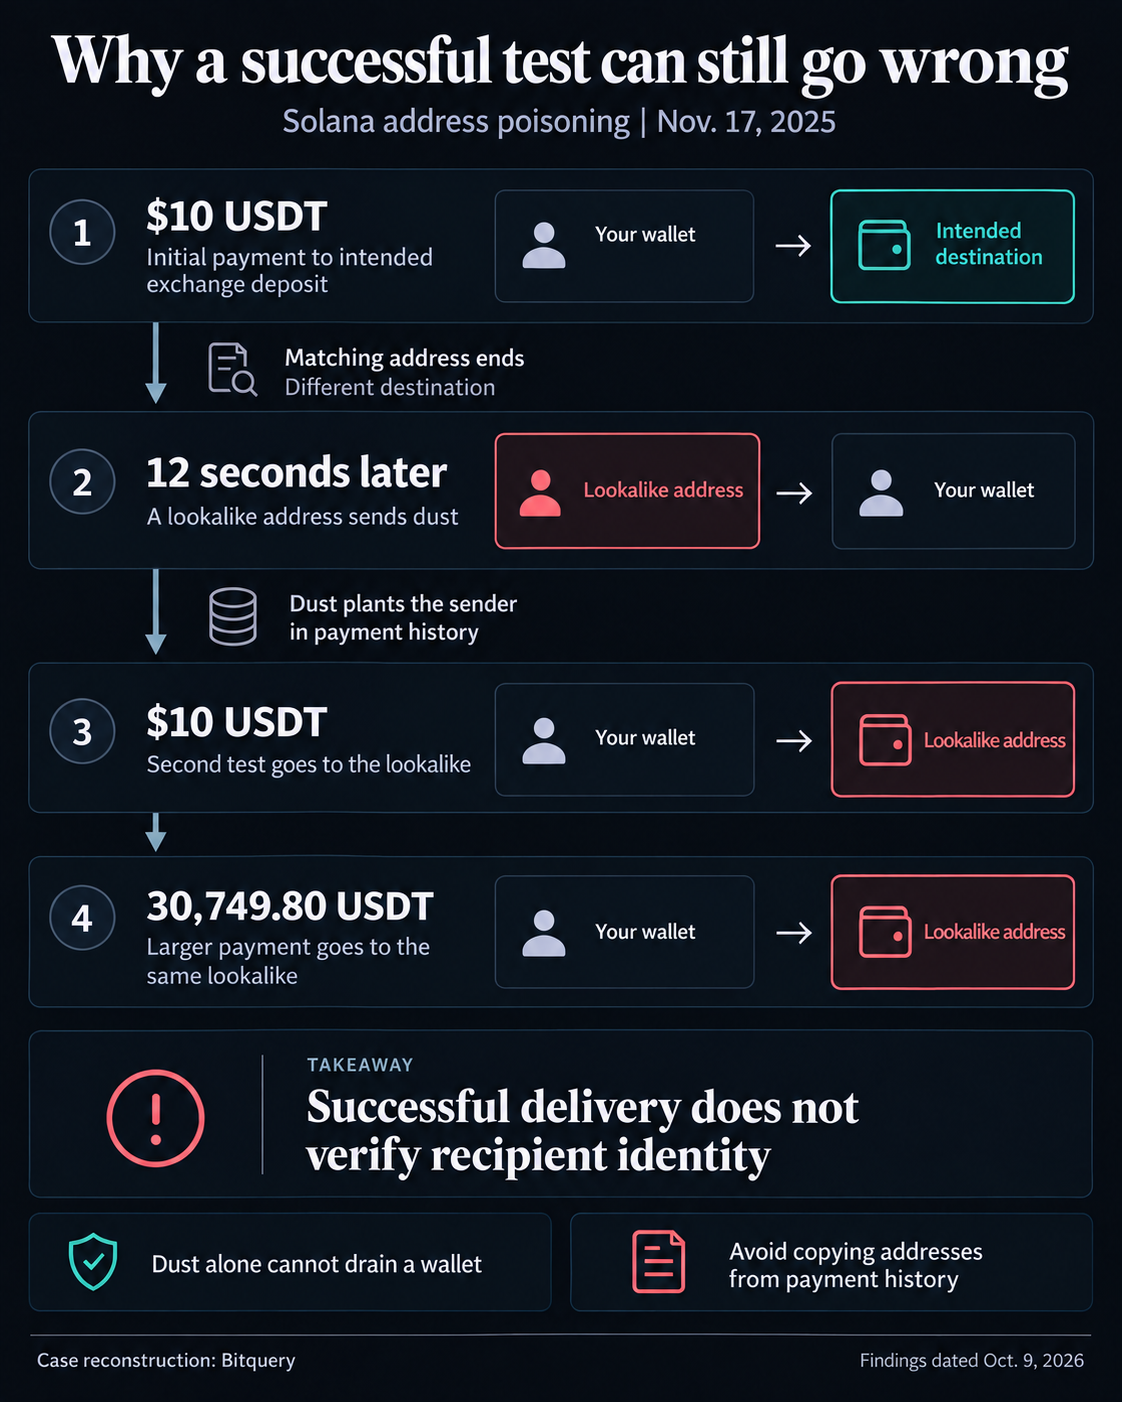
The implication is that a successful test confirms delivery to the selected address, but cannot establish who controls it. If the destination was copied incorrectly, repeating the payment repeats the mistake.
Receiving dust does not itself drain a wallet in this mechanism. The loss occurs when its owner subsequently authorizes a payment to the lookalike.
Bitquery counted 4,497,798 targeted wallets from Oct. 30, 2025, through Oct. 7, 2026. Its rule required a same-day payment of at least $1 in SOL, USDC or USDT, followed by dust or a fake stablecoin token from a different address matching at least three characters at each end of the payee.
The loss analysis used a smaller subset: approximately 3.0 million wallets poisoned through July 9, 2026. Of those, 1,104 made qualifying payments totaling $940,106. The wider targeting count does not mean 4.5 million wallets lost money.
The loss total is a floor. It counts payments of at least $1 within 90 days of the first dust. Beyond that window, a payment could qualify if more dust arrived that day. Wallets poisoned after July 9 and payments outside those rules were excluded. Bitquery also removed likely existing relationships, such as pairs with earlier payments or repayments; some genuine thefts may have been excluded.
Phantom’s address-poisoning guidance advises avoiding addresses copied from transaction history and verifying the address before sending.
Its receiving-payment instructions separate the checks: first confirm the exact recipient address and network, then look up the transaction status on an explorer. Phantom also says it cannot recover tokens sent to the wrong address.


Be the first to comment